One infrastructure record. Connected security evidence.
Vista Platform is a self-hosted infrastructure inventory and DCIM platform with cryptographic posture built in. It connects sites, racks, cabling, IPAM, software, and relationships to discovery, evaluation, action, and proof. Identity evidence remains visible, and ambiguous observations can remain provisional.
Sites, floor plans, rack elevations, power budgets, lifecycle records, IPAM, and cable traces belong to the same asset record as ownership and cryptographic findings. Core includes the complete internal workspace. Enterprise adds synchronization with supported external systems.
Illustrative infrastructure context; not a product screenshot.
Unification happens in the inventory—not just in the interface.
Each discovery channel sees a different part of the estate. Vista normalizes those observations at ingest, so dashboards, compliance controls, tickets and CBOM artifacts all work from the same canonical record.
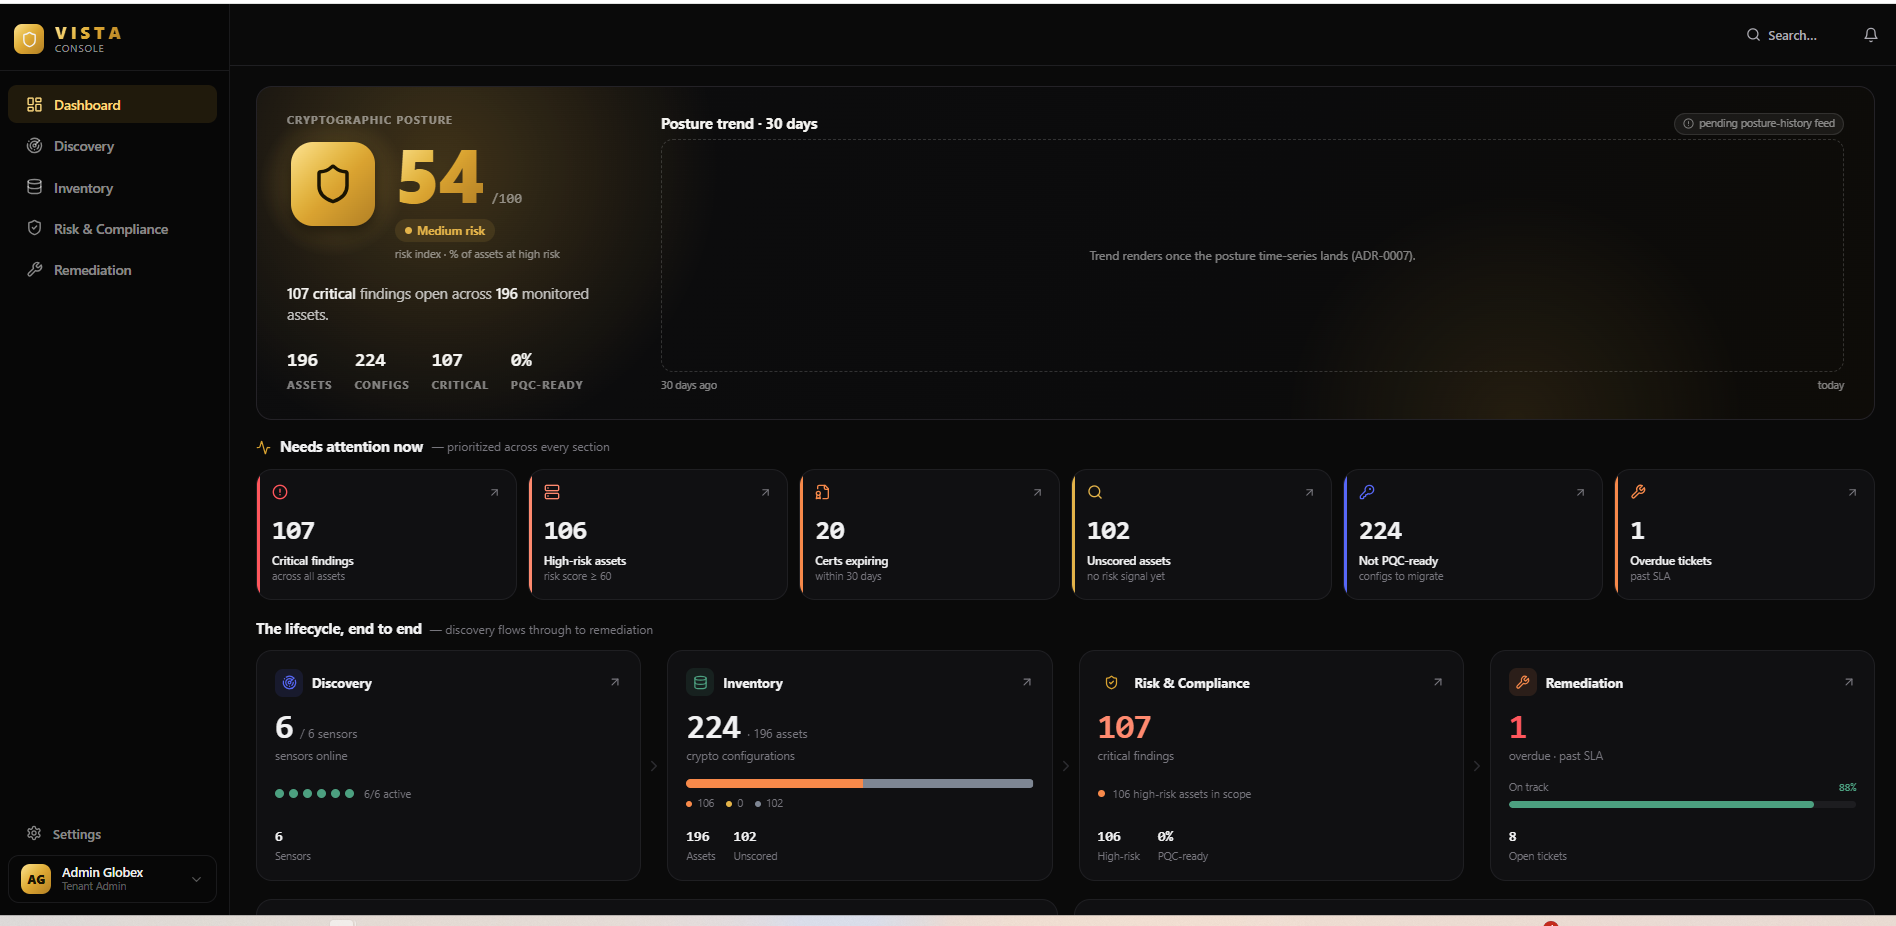
The operating view connects cryptographic posture to the assets, locations, network context, findings and remediation work underneath it—so a score is always a path into evidence and action.
Vista Console shown with illustrative environment data. Product interface will continue to evolve.
Continuous cryptographic assurance
From observation to accountable action.
01 · DISCOVER
See traffic, configuration and cloud posture.
Observe live cryptographic use passively, target known coverage gaps on demand, interrogate supported appliances for loaded-but-idle configuration, and query cloud-provider APIs without deploying agents into every workload.
02 · UNIFY
Resolve findings into one operating inventory.
Normalize certificates, keys, algorithms and configurations into a shared model. Deduplicate certificates by fingerprint and preserve which channels observed each asset.
03 · EVALUATE
Score the cryptography—not just the host.
Apply a curated algorithm taxonomy, continuous compliance controls and quantum-readiness measurements to the inventory itself, with findings that update as observations change.
04 · ACT
Turn findings into owned remediation.
Raise stateful, deduplicated alerts; preserve an evidence chain; and convert work into tickets that retain their connection to the condition that created them.
05 · PROVE
Generate reproducible CBOM evidence.
Define a versioned scope, freeze the inventory into canonical CycloneDX 1.7 bytes, record provenance and freshness, and export CycloneDX evidence. Enterprise adds SPDX and PDF projections.
CORE CAPABILITY
Start with the real platform.
Core includes discovery, the complete internal DCIM and IPAM workspace, continuous compliance evaluation, PQC assessment and CBOM generation—with no asset, sensor, seat or time cap.
Evidence with a boundary and a timestamp
A CBOM should answer more than “what was in the report?”
Vista treats the CBOM as a first-class artifact. The record says which versioned scope it represents, when it was generated, how fresh its underlying observations were and which canonical bytes produced its content hash.
Defined scopeA reusable boundary, versioned independently from the snapshot.
Canonical bytesDeterministic CycloneDX 1.7 content with a stable identity.
Recorded provenanceScope, generation time and input-data freshness travel with the artifact.
Multiple projectionsCore exports CycloneDX; Enterprise adds SPDX and PDF from the canonical source.
Edition boundary: Core generates, hashes and exports CBOM artifacts. Enterprise adds Ed25519 signing, compliance-attestation layers and artifact comparison.
Operate the migration
Make post-quantum readiness a measurable program.
Vista classifies the inventory into PQC-ready, symmetric-safe, needs-migration, and not-yet-assessed categories, evaluates readiness through typed controls, and keeps the work connected to evidence.
01InventoryFind classical and post-quantum cryptography in context.
02PrioritizeUse algorithm-family worklists and separate classical public-key exposure from symmetric use.
03RemediateAssign alerts and tickets to the teams that own the dependency.
04EvidenceCapture milestone CBOMs and repeat against the same boundary.
What Vista does: inventory, classify, recommend and track. What it does not do: generate PQC keys, reissue certificates or perform the migration for you.
Clear commercial boundaries
One platform. Three editions for different operating models.
CORE
Discover, evaluate and generate evidence.
Every standard discovery channel
DCIM, IPAM, cabling, circuits, and virtual infrastructure
Canonical inventory and algorithm taxonomy
Continuous compliance and PQC readiness
CBOM generation and export
RBAC, audit logging and tenant isolation
ENTERPRISE
Add regulated and federated operations.
CBOM signing, attestation and comparison
Tenant OIDC single sign-on
NetBox synchronization, CMDB and SIEM integration
Model-backed query and remediation drafts
Signed regulated-framework catalog
MSP
Operate a customer management plane.
Everything in Enterprise
Tenant lifecycle management
Cross-tenant commercial management
Billing operations
Cross-tenant views
Designed for defensible answers
Coverage you can explain.
Vista reports what its deployed discovery channels observe and shows the freshness and coverage signals behind that knowledge. It does not infer that an unobserved segment contains no cryptography.
Active Scan targets assets you select; it is not an unrestricted network or vulnerability scanner.
Device interrogation is read-only and limited to supported APIs and the credentials you provide.
Host collection is opt-in; coverage depends on the discovery channels you connect and authorize.
Self-hosted operation keeps the inventory and evidence inside your infrastructure.
See your own estate
A real inventory is more persuasive than a polished demo dataset.
Show us the environment you need to understand. We will help define the first useful boundary and the evidence that should come out of it.
Run Vista Platform Core on your own infrastructure at no charge. The platform is proprietary; the passive sensor and device interrogation agent are Apache-2.0. Enterprise adds paid integrations, identity, and evidence capabilities. MSP adds the operating tools for serving customers.